When a Cyber Incident Happens: What Should an SME Tell Employees, Customers and Partners?
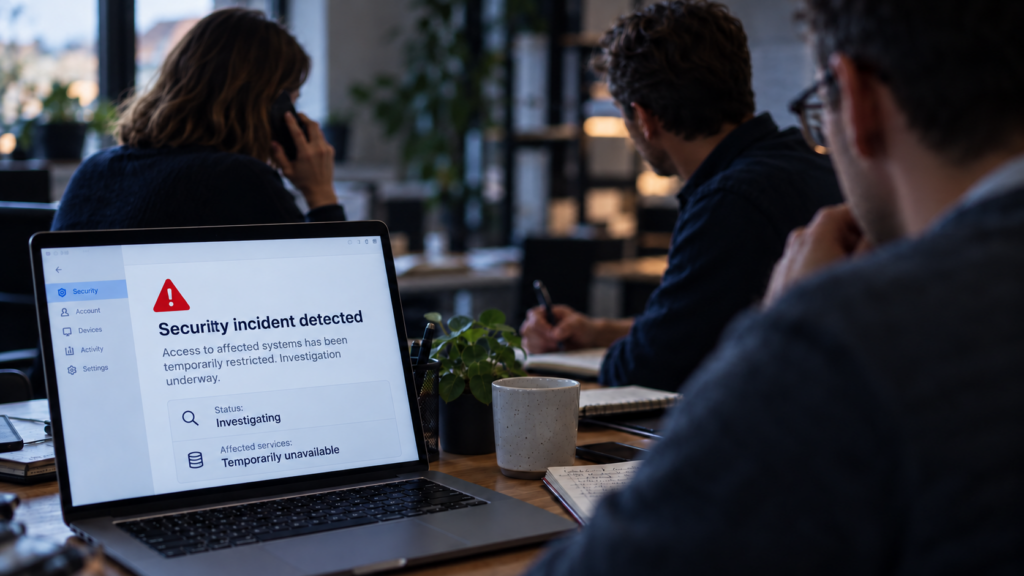
Customers are receiving unusual emails from the company. Employees cannot access shared systems. An IT provider is investigating, but the extent of the problem is still unclear. Meanwhile, someone must decide what to tell the people whose work, information or services may be affected.
During a cybersecurity incident, the need to communicate often arises before the investigation provides a complete explanation. For an SME, this can be particularly demanding: the person coordinating the response may also be managing operations and answering customers.
Communication has practical consequences. Employees need instructions, customers may need to protect themselves, and partners must understand whether their activities are affected.
Communicating before everything is known
Early in an incident, a business may know that unauthorised access occurred without knowing which information was affected. Waiting for a complete picture can leave people without necessary guidance. Offering reassurance too soon can create promises the investigation later contradicts.
A credible initial message distinguishes confirmed facts from unanswered questions. It explains the response underway, gives relevant instructions and indicates when further information will follow.
“We are investigating whether personal information was affected” conveys a different level of certainty from “No personal information was affected.” Clear wording allows the business to update its account as evidence emerges without undermining earlier statements.
Internal coordination shapes external credibility
If management, technical support and customer-facing staff have different understandings of the incident, contradictory information can quickly reach the public.
An SME needs clear communication ownership: someone coordinates messages, technical findings are validated, and relevant expertise is involved where privacy or notification questions arise. Staff handling enquiries should know what they can confirm and where to direct unanswered questions.
Employees also need operational guidance, such as whether to stop using a service, follow a temporary process or report suspicious activity through a designated channel. Communication arrangements should remain usable if normal email or shared systems are unavailable.
Different audiences need different answers
Consistency means keeping the facts aligned while addressing each audience’s needs.
Employees need to understand how to work safely and respond to enquiries. Customers need to know whether their information or access to services is affected, what protective action to take and where to obtain help. Partners may need to assess disrupted services, shared systems or messages that can no longer be trusted.
The starting point is the decision each recipient faces. A technically accurate account can still be unhelpful if it leaves those practical questions unanswered.
Reassurance needs evidence and empathy
“We take cybersecurity seriously” offers little assistance to someone worried about their data. Reassurance becomes more credible when supported by confirmed actions, such as restricting access to affected systems, engaging specialists or providing an alternative service.
Empathy should acknowledge the actual consequences: interrupted work, uncertainty about personal information or difficulty accessing support. It gives factual information a human context.
Explaining that attackers caused the incident does not resolve questions about the business’s response. People will also judge whether it acted promptly and helped those affected. Describing an incident as “minor” before its consequences are understood can weaken that confidence.
Communication continues through recovery
An initial statement begins an ongoing conversation. Updates should reflect new findings, confirm whether existing instructions still apply and explain when further information is expected. Customer support and other teams need updated guidance alongside public messages.
Repeated questions can reveal unclear explanations or overlooked concerns. Listening helps the business improve communication during the response.
Transparency also requires judgement. Meaningful disclosure should be coordinated with technical and professional advice to avoid exposing sensitive information or interfering with containment.
Preparation makes these decisions easier. Before an incident, an SME can establish communication responsibilities, alternative channels and approval arrangements, then test them through a short exercise.
SOC services and technical providers can supply findings that inform messages. The business must translate those findings into understandable explanations and useful instructions. Clear communication helps people act while the investigation develops and gives them a credible basis for assessing the organisation’s response.
Sources
Llamas Covarrubias, J. Z. (2025). Effective Communication as a Pillar of Cybersecurity: Managing Incidents and Crises in the Digital Era. Journal of Risk Analysis and Crisis Response, 15(2), 239–272.
Wang, P., & Park, S.-A. (2017). Communication in Cybersecurity: A Public Communication Model for Business Data Breach Incident Handling. Issues in Information Systems, 18(2), 136–147.
Citrawijaya, O. R., Susanto, B. K., & Amalia, D. A. (2024). The Role of Communication Strategies in Crisis Management: A Comparative Analysis Across Industries. The Journal of Academic Science, 1(6), 748–761.